10 IT Asset Tracking Best Practices: Inventory, Tag, Audit and Retire Every IT Asset

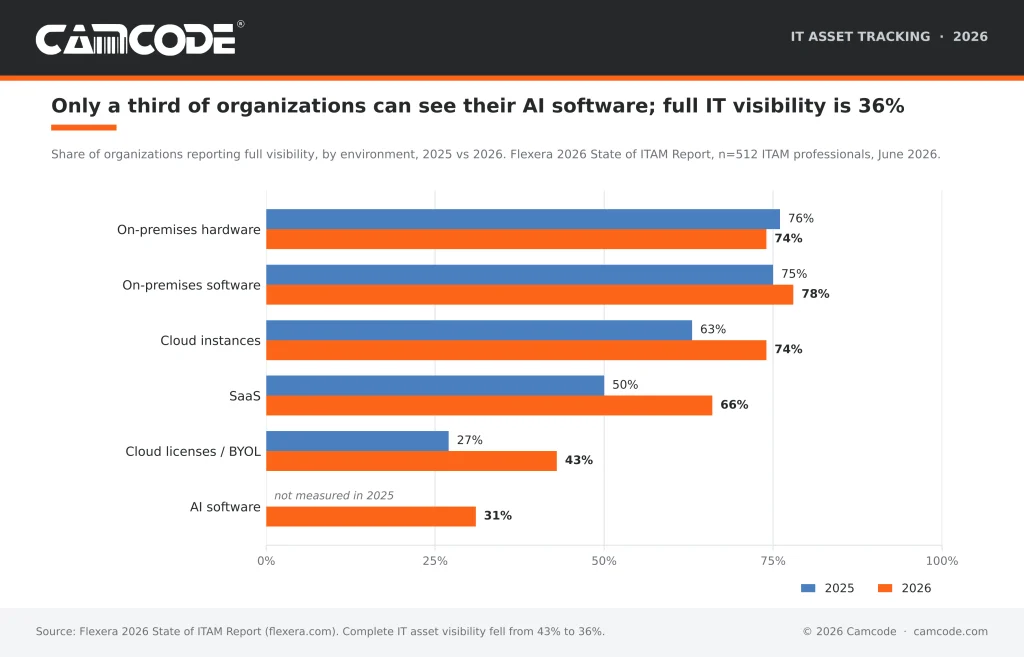
Only 36% of organizations have complete visibility into their IT assets in 2026, down from 43% in 2025, according to Flexera’s 2026 State of ITAM Report, which is why IT asset tracking best practices matter more than the tracking software you buy. The best practices for IT asset tracking are ten habits:
The same Flexera survey of 512 ITAM professionals found 78% of ITAM teams rank maintaining an accurate inventory as their top priority, which means most teams know the problem and have not solved it.
The cost of not knowing is measurable. WanAware’s 2025 ITAM Confidence Gap survey of 600 IT and operations professionals estimates that up to 25% of IT spend goes to ghost assets, devices and licenses that stay on the books after they stop being used.
On the software side, Zylo’s 2026 SaaS Management Index found 46% of SaaS licenses sit unused in a typical 30-day period, about $19.8 million a year for the average organization in its dataset.
IT asset tracking and management fixes both problems by giving every laptop, server, phone, peripheral and license a unique ID, an owner, a location and a lifecycle state, then keeping that record current from purchase to disposal.
Done well, it pays for itself by:
Not happy with your company’s current IT asset tracking process? The ten best practices below are sequenced in the order most IT teams should tackle them, starting with the one decision everything else depends on.
IT asset tracking is the process of recording every piece of IT hardware and software an organization owns, assigning each one a unique identifier and keeping its location, custodian, condition and lifecycle stage current from purchase to disposal.
Hardware tracking covers laptops, desktops, servers, network gear, phones, tablets, monitors and peripherals. Software tracking covers installed licenses, SaaS subscriptions and the entitlements attached to them.
IT asset tracking is the data layer of IT asset management (ITAM): ITAM decides what to buy, how to use it and when to retire it; tracking supplies the record those decisions run on.
Most organizations run it with a barcode or RFID label on each physical asset, an agent or network discovery tool for anything that connects to the network and asset tracking software that ties the two together.
For tracking methods across every asset class, not only IT, see our guide to what asset tracking is and how it works.
Every IT asset tracking program starts with a single source of truth: one inventory that lists every hardware device, software license and cloud subscription the organization owns, who holds it and where it is. Spreadsheets split by department are the most common reason assets go missing, because nobody owns the master list.
WanAware’s survey found 65% of IT managers use six or more tools for asset management while a quarter still run core workflows on spreadsheets and email. The CIS Critical Security Controls make the centralized inventory Safeguard 1.1: an accurate, detailed and up-to-date inventory of every enterprise asset that can store or process data, with the network address, hardware address, machine name, owner and department recorded for each.
Pick the system of record first (an ITAM platform, a CMDB or dedicated asset tracking software), name the person who owns it and route every purchase, hand-off and disposal through it. Everything else on this list depends on that one decision.
The idea of trying to locate every asset within your company can be daunting. We’re not just talking about desktop computers. You need to locate every desk phone, mobile device, personal printer and even company-issued headset currently in use within your organization.
Narrow things down by using the discovery tools already on your network to locate connected assets. Methods of doing this include:
These steps should help you identify a large portion of your inventory. Follow up by confirming with employees that they’re currently in possession of specific assets.
Finish off with a floor-to-floor sweep for any assets that might be offline or not hooked up to software capable of tracking it, which can also help to identify shadow IT hardware.
Set the audit cadence before the first audit ends. CIS Safeguard 1.1 calls for reviewing the full inventory at least twice a year. CISA’s Binding Operational Directive 23-01 goes further for federal civilian agencies: automated asset discovery every 7 days and vulnerability enumeration every 14 days, laptops and other roaming devices included.
A workable schedule for most organizations is automated discovery weekly, a physical scan of each site twice a year and a scan of any asset the moment it changes hands.
Once you’ve located each of your company’s assets, start pulling identifying data from each one. The most important information you should be gathering includes:
Having this information in place allows managers and other executives to properly assess additional equipment needs. They’ll know whether they already have the equipment in-house or whether it actually needs to be purchased.
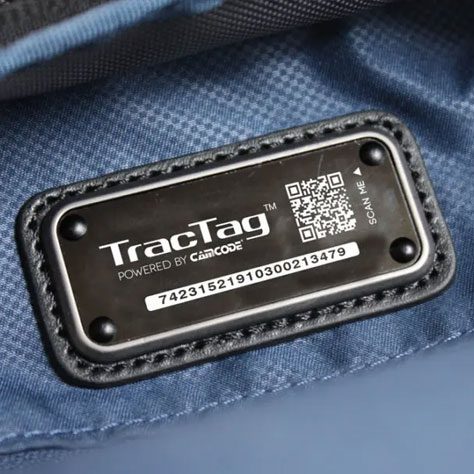
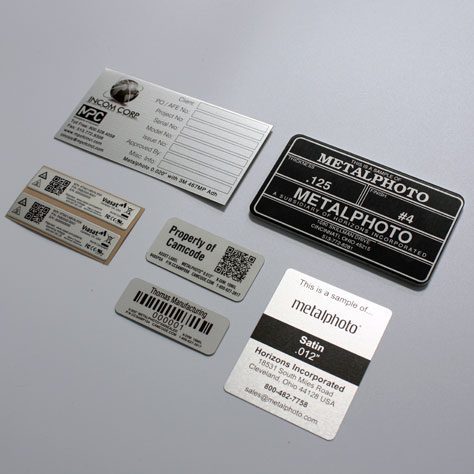
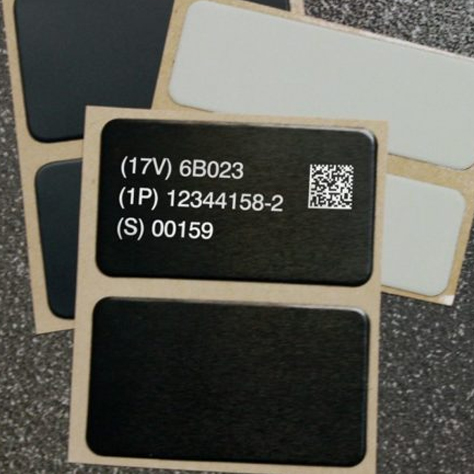
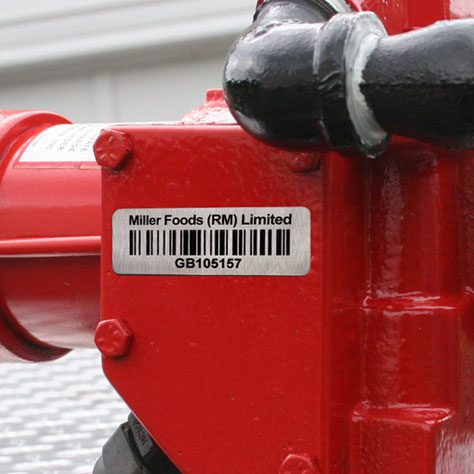
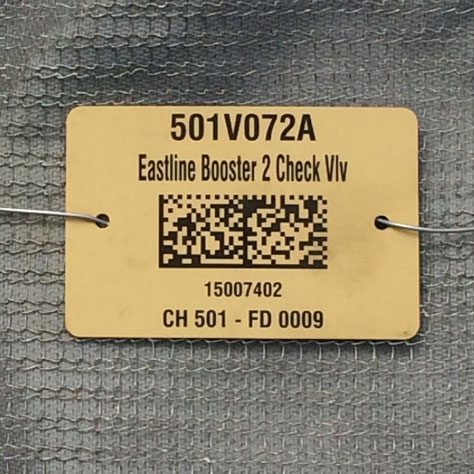
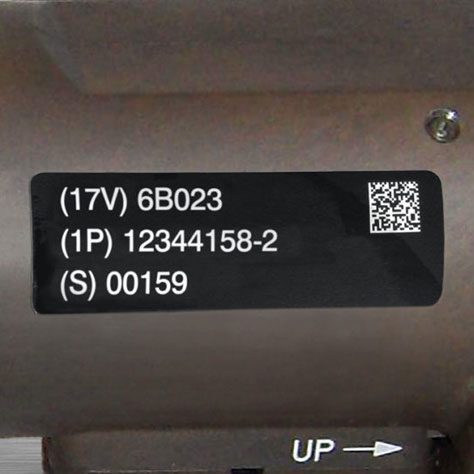
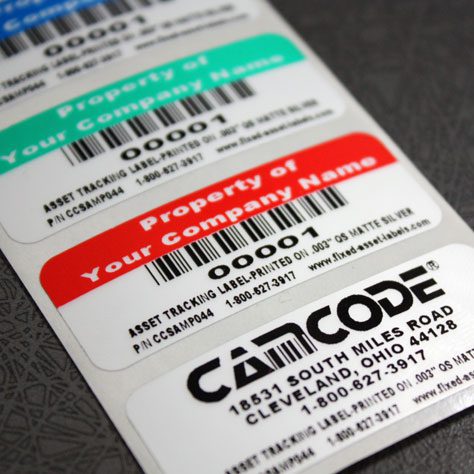
A barcode label is what turns an inventory row into something a technician can verify in two seconds. Give every physical IT asset a label that carries a unique asset ID in a barcode (Code 128 or a QR code for small devices) and the same ID in human-readable text, then store every other attribute in your asset tracking software solution, not on the label.
The ID stays fixed for the asset’s whole life while the record behind it changes, so never encode a location, owner or description in the barcode itself. Pre-printed labels in a numbered series cost less than print-on-demand and stop two technicians from issuing the same number.
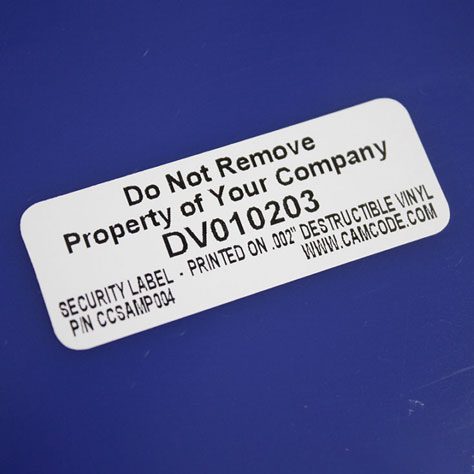
Match the label to the asset and its environment:
Put the label in the same spot on every asset of the same type (bottom case on laptops, rear panel on monitors, front bezel on rack servers) so audits never involve turning equipment over.
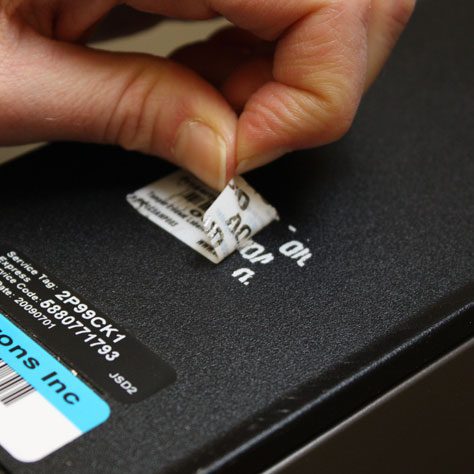
(Useful tip: If theft or tampering is a concern, security tags can help to deter these activities.) For a longer look at materials and formats, see what asset tags are and how to choose them.
Lifecycle tracking follows each IT asset from procurement to disposal and records the date and the responsible person every time its state changes. Lay the stages out (requested, approved, received, deployed, in use, in repair, in storage, retired, disposed), assign one status value to each and require the record to change state before the asset physically moves.
Then use those states to see where any asset sits today.
The lifecycle of different assets will vary. Sometimes workstations might be put to use for a few months for a contractor, then placed in storage until needed again. Certain users might upgrade to a different version of the software, freeing the older version up for use by another employee.
Track exchanges of this type carefully. Retirement needs the same discipline as deployment: record the data-wipe method and certificate before a device leaves the building, because a decommissioned laptop with its drive still in it is a data breach that has not happened yet.
Make sure you have clear-cut procedures in place when it comes to checking out, assigning and decommissioning assets. Don’t allow passage from one department to another without enforcing some type of standards on:
Consider establishing a specific department responsible for these processes. Smaller companies should still designate roles for IT asset tracking to certain employees or areas.
Offboarding is where most hardware disappears. Teqtivity’s Q1 2026 IT Asset Intelligence Report cites HR survey data showing 71% of HR professionals report at least one departing employee did not return a company device. Make device return a required step in the offboarding checklist, update the record the same day and escalate any device not scanned back within five business days.
Hiren Hasmukh, founder and CEO of IT asset management platform Teqtivity, put the offboarding gap in security terms when the company released its Q1 2026 report:
“Security controls are only as good as the asset inventory underneath them. You can’t patch a device you can’t find. You can’t revoke access on a device you don’t know is active.”
– Hiren Hasmukh, Founder and CEO, Teqtivity. Cybersecurity Dive press release, May 5, 2026
That is the case for treating an unreturned laptop as an open incident rather than a missing row.
Software licenses and SaaS subscriptions belong in the same IT asset inventory as the hardware they run on. They are also where the money leaks. Zylo’s 2026 SaaS Management Index puts average license utilization at 54%, with 46% of seats unused in a typical 30-day period and nine new applications entering the average portfolio every month.
Flexera’s 2026 report adds the compliance side: 48% of organizations were audited by a software vendor in the past year, 44% spent more than $1 million on audits over three years and Microsoft audited 64% of them.
Track every license and subscription with its product, edition, seat count, assigned users, renewal date, cost center and contract terms. Reconcile seats against actual logins quarterly and reclaim anything idle for 30 days or more. Tie SaaS deprovisioning to the same offboarding checklist as device return, so a departed employee’s seats come back at the same time as the laptop.
The newest license category is the least tracked. Only 31% of organizations in the Flexera survey have visibility into AI software. Becky Trevino, Flexera’s chief product officer, described the pattern when the report was released:
“AI is changing the economics of IT faster than most organizations can adapt. What we’re seeing is a familiar pattern of rapid adoption followed by a scramble for visibility and control, as spend surges.” – Becky Trevino, Chief Product Officer, Flexera. Flexera press release, June 24, 2026
Add AI subscriptions to the license inventory now, while the count is small enough to reconcile by hand.
One overlooked aspect of IT asset tracking is ensuring items meet established standards.
Your IT asset tracking process can be turned into a valuable tool in keeping your organization secure. CISA’s Binding Operational Directive 23-01 states that “asset discovery is a building block of operational visibility”; you cannot patch, encrypt or wipe a device that is not in the inventory. Record encryption status, patch level and the endpoint agent present on every device as inventory fields.
Treat any device the discovery scan finds but the inventory does not as an incident, not a data-entry task. Initiate periodic audit inventories and make cataloging this type of information part of your standard procedures.
Integrating IT asset tracking with your ITSM service desk, CMDB and finance system means every ticket, configuration item and ledger entry references the same asset ID. Connect the inventory to the service desk so incidents, changes and requests carry the asset ID; to the CMDB so configuration items inherit it; and to finance so the fixed asset register, the depreciation schedule and the physical count reconcile against one list.
Flexera reports that 78% of organizations now have a FinOps team and that ITAM and FinOps reporting alignment rose five percentage points in 2026, which is the direction the integration should run: tracking data flowing into cost decisions. WanAware’s survey shows the gap integration closes: 95% of IT leaders trust their asset data, but only 35% of managers outside IT do.
Jeff Collins, CEO of WanAware, on what that trust gap costs:
This isn’t just a perception problem, it’s an operational one. When confidence in IT asset data drops by half outside the IT department, it creates real risk, wasted spend, and delays that fly under the radar until it’s too late.”
– Jeff Collins, CEO, WanAware. ITOps Times, August 13, 2025
Finance and operations will trust the inventory when it is the same list their own systems read from.
Initiating IT asset tracking with manual processes opens you up to a greater risk of human error. It’s also harder to coordinate the status of equipment between different departments. Employing an automated process allows you to integrate your asset tracking with other company systems.
Three layers of automation cover most estates:
Discovery alone misses spare stock, decommissioned units and anything offline, which is why the physical scan stays in the process.
This allows other areas to easily retrieve data for their own uses, like pulling reports or drawing up budgets. It also facilitates collaboration with other team members responsible for loading and validating asset data.
Answer ten questions, one per best practice above. The scorecard grades your program, ranks the three practices to fix first and links you to the section for each.
CAMCODETen questions, one per best practice. Pick the answer closest to how things work today.
Setting up an IT asset tracking system takes five steps: choose the system of record, define the data standard, label and scan everything in a baseline audit, connect discovery and workflows, then schedule the audits that keep the record accurate.
Most IT estates end up using three of these together: discovery for whatever is on the network, barcode labels for physical custody and the tracking software that joins them.
CAMCODE| Method | Best for | Strengths | Watch out for | Verdict |
|---|---|---|---|---|
| SpreadsheetManualCost: none | Fewer than about 50 assets at one site | Free and familiar; fine as a starting list | No scan verification, no history, breaks the first time two people edit it | Outgrown fast. Move to one system of record (Practice 1) before the first audit. |
| Barcode or QR labels plus scannersPhysical custodyCost: lowest per asset | Every physical asset, every site: laptops, monitors, phones, servers | Two-second verification, works offline, any phone or handheld can scan, label lasts the life of the asset | Needs a line of sight; the label material has to match the asset and its environment (polyester for handled devices, tamper-evident where swapping is a risk, metal foil for racks) | The baseline. Every other method confirms what is on the network or where it is; this one confirms who has it. |
| RFID tagsBulk readsCost: higher tags and readers | High-volume audits, server rooms, equipment cages and assets that move often | Reads dozens of tags per second without line of sight | Metal and liquids interfere unless you use on-metal tags; readers add a second budget line | Add it where you count hundreds of assets at once. Keep the barcode on the asset as well. |
| Agent or network discoveryAutomatedCost: software license | Anything that connects to the network, plus the software installed on it | Finds devices and software automatically with no labor; feeds patch and license data | Misses offline, spare and retired equipment; cannot say who physically has a device or where it sits | Run it weekly. Reconcile it against the physical scan, never instead of one. |
| GPS or BLE trackersLive locationCost: hardware plus subscription | Field equipment and high-value mobile assets that leave the building | Live location and movement alerts | Battery life and subscription cost; more than office hardware needs | Reserve for the few assets whose location changes daily. |
IT asset tracking fails in the gaps between systems, not inside them. The laptop that never came back, the license renewed for someone who left in March, the server finance is still depreciating two years after it was pulled from the rack: each one is a hand-off nobody recorded.
The ten practices above close those gaps in a specific order. Build one inventory and audit it first, because every later step writes to that record. Label every physical asset, because a barcode is the only method that confirms who has a device rather than what is on the network. Then add the rules, the license tracking, the security fields and the integrations that keep the record true after the audit team goes home.
If your scorecard came back “Ad hoc” or “Developing”, start with Practices 1 and 4 this quarter and schedule the first physical count before you buy anything else. If it came back “Managed”, the remaining money is almost always in Practices 6, 7 and 9: offboarding, licenses and integration. Either way, publish record accuracy as a monthly number. A team that can say “94% of our assets were verified in the last 180 days” has IT asset tracking; a team that cannot has a list.
Camcode makes the labels for the physical half of this: polyester asset tags for the devices people carry, tamper-evident labels for the ones that walk, and metal foil labels for the racks. Request free samples and test them on your own hardware before you order a numbered series.
IT asset tracking is the record-keeping layer: it identifies each hardware and software asset, assigns it an ID and keeps its location, owner and lifecycle state current. IT asset management (ITAM) is the broader discipline that uses that record to decide what to buy, how to deploy it, when to renew or retire it and how to stay compliant.
You cannot run ITAM without tracking; tracking without ITAM is a list nobody acts on. Our complete guide to IT asset management covers the management side.
Audit IT assets on three cadences: automated discovery at least weekly, a physical scan of every site at least twice a year and a scan every time an asset changes hands. The CIS Critical Security Controls require reviewing the enterprise asset inventory at least bi-annually. CISA’s BOD 23-01 requires federal civilian agencies to run automated discovery every 7 days.
Organizations with high device turnover, such as those with large contractor populations, should count more often.
At minimum: a unique asset ID, serial number, make and model, manufacturer, purchase date, cost and PO number, warranty end date, assigned user, department, physical location, condition and lifecycle stage. Software records add license key, edition, seat count, assigned users, renewal date and cost center.
Security teams also want encryption status, patch level and the endpoint agent installed.
A ghost asset is a device or license that still appears in the inventory or on the fixed asset register but is no longer in use, has been lost or stolen or was never returned.
WanAware’s 2025 survey estimates up to 25% of IT spend is wasted on ghost assets. They inflate support contracts, insurance and depreciation. An unreturned laptop that still holds credentials is a security exposure, not only an accounting error.
Barcode labels are the default for IT hardware: they cost the least per asset, any phone or handheld scanner can read them and a polyester or tamper-evident label survives years of handling on a laptop or monitor.
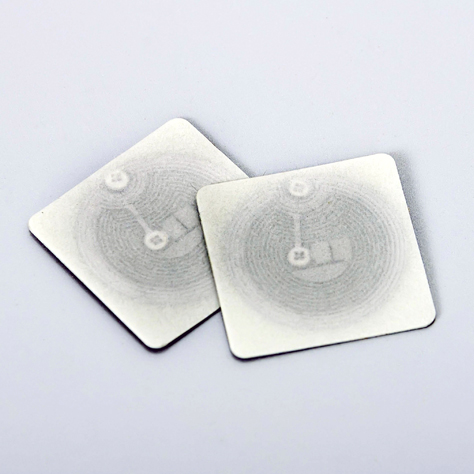
RFID earns its higher tag and reader cost where you audit hundreds of assets at once or need to read tags without line of sight, such as a server room or an equipment cage. Many organizations use both, with RFID tags on high-value or high-volume assets and barcodes on everything else.
Apply the barcode label and scan the laptop to the employee’s record before it ships, require a scan or photo confirmation on receipt, let the endpoint agent report check-ins while the device is in use and send a prepaid return kit at offboarding with a deadline.
Teqtivity’s Q1 2026 report found 71% of HR professionals have had at least one departing employee keep a company device, so the return step needs an owner and an escalation path, not an email reminder.
Our sales engineers are experts in automatic asset tracking, tagging and identification, and can answer all your questions. Get in touch now.
Lets Talk ›Enter your information and get a free checklist of the top questions to answer and tips to plan a successful asset tagging project for any asset management or tracking system implementation.